CURRENT EDITION: Security+. Start with Season 2 for the updated certification preparation course. Previous seasons are archived and may not reflect current exam requirements.
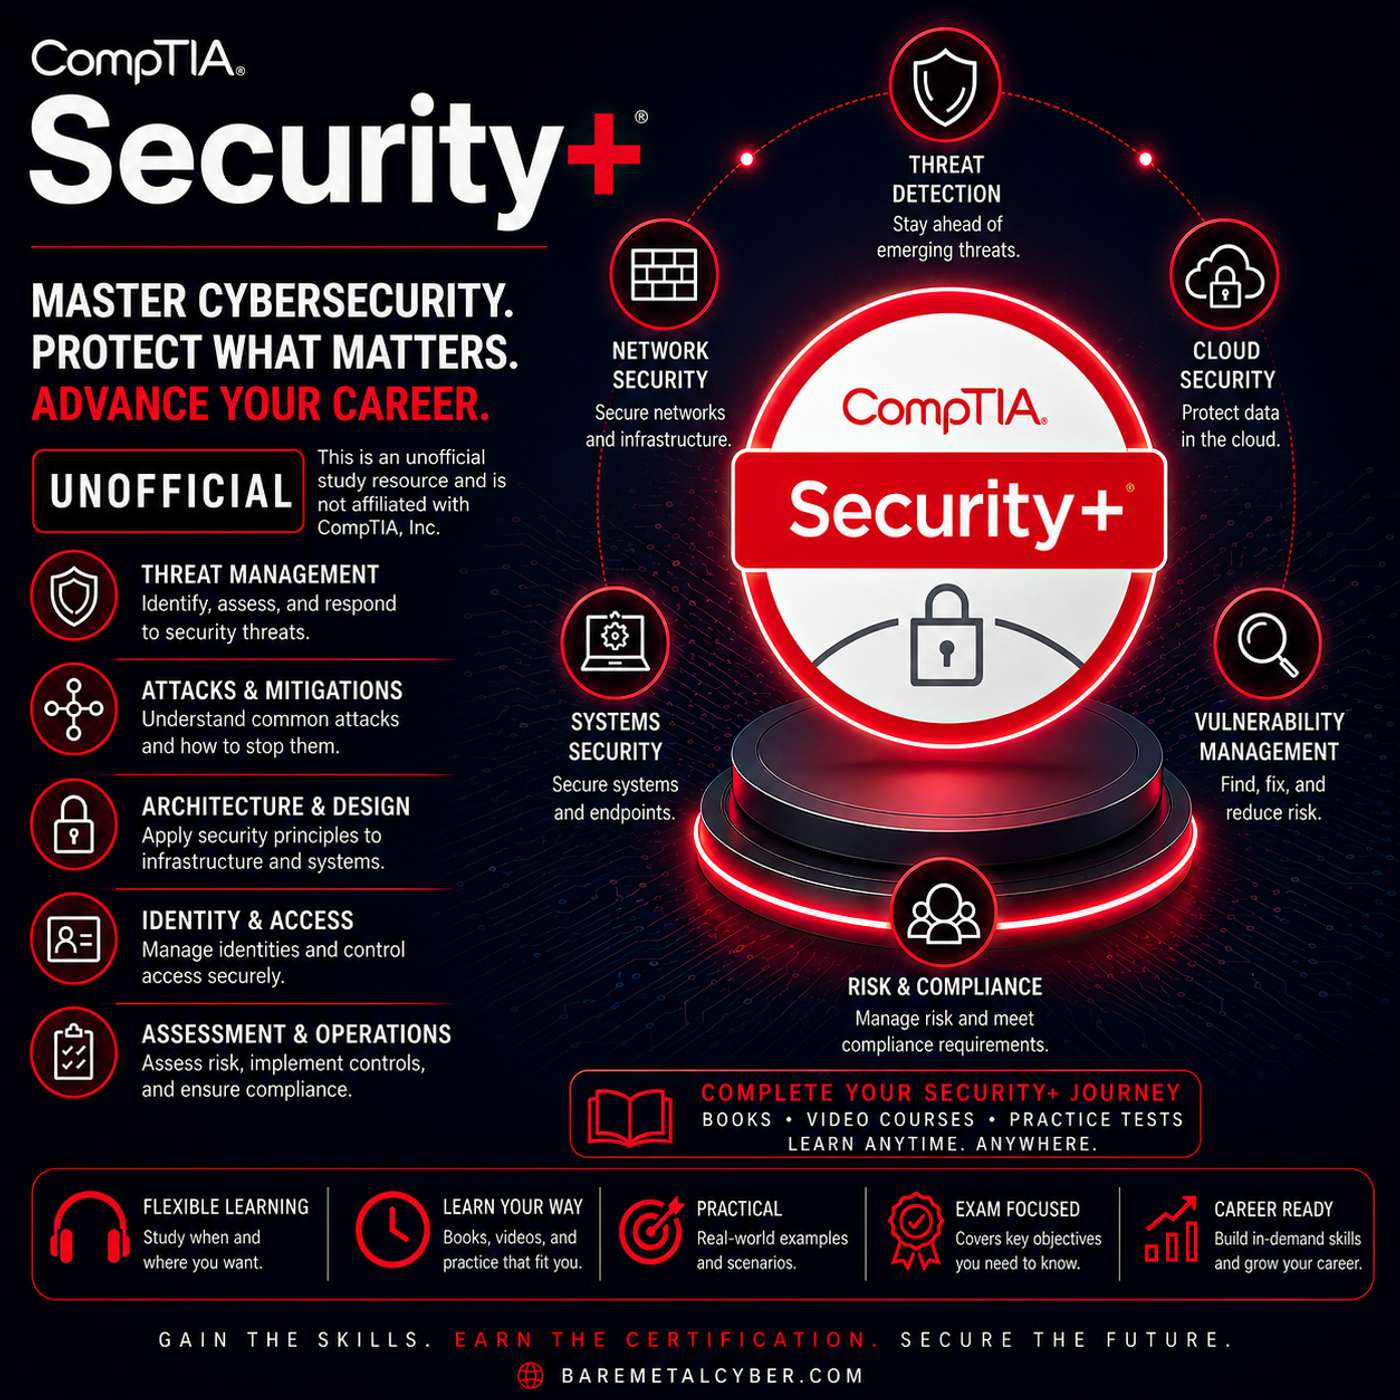
Certified - Security+ is your completely free audio companion for mastering the CompTIA Security+ certification exam. Developed by BareMetalCyber.com, this immersive Audio Course transforms every domain of the official exam objectives into clear, practical, and exam-ready lessons you can learn anywhere—whether commuting, exercising, or studying at home. Each episode delivers focused explanations, real-world examples, and proven study strategies designed to build confidence and help you pass on your first attempt. Structured for busy professionals and new learners alike, the series provides a complete, flexible way to prepare for certification success without relying on slides or handouts.
The CompTIA Security+ certification is the global benchmark for validating essential cybersecurity knowledge and hands-on skills. It covers critical areas including threat identification, risk management, network security, identity and access control, incident response, and cryptography. Designed to meet the latest industry and Department of Defense (DoD) requirements, Security+ ensures you can assess environments, implement controls, and secure systems in real-world settings. It serves as the perfect foundation for cybersecurity careers and advanced credentials like CySA+, CASP+, and C I S S P. Recognized by employers worldwide, Security+ demonstrates your readiness to protect data, defend networks, and operate confidently in modern cyber defense roles.
For a deeper study experience, pair this Audio Course with the companion textbook Achieve CompTIA Security+ SY0-701 Exam Success—the concise and complete guide designed for busy professionals preparing to earn their certification. Together, they form a powerful toolkit to help you understand, retain, and apply cybersecurity principles from day one through exam day.
Site
RSS
Apple
Data updated on 16/11/2026
Recent rankings
Latest chart positions across Apple Podcasts and Spotify rankings.
Shared links between episodes and podcasts
Links found in episode descriptions and other podcasts that share them.
Discover shows related to Certified: The CompTIA Security+ Audio Course, based on actual content similarities. Explore podcasts with similar topics, themes, and formats, backed by real data.
Final Objectives Update: What Changed When CompTIA Finalized SY0-801 (Update)
Season 2 · Episode 118
Wednesday, July 15, 2026 • Duration 14:12
CURRENT EDITION: Security+. This episode is part of Season 2, the recommended course for the current certification exam.
This episode is reserved for final updates after CompTIA finalizes the SY0-801 exam objectives. Its purpose is to identify what changed from the draft objectives, including added topics, removed topics, renamed terms, reorganized objectives, weight changes, or clarified wording that affects study priorities. Students should use this episode as a fast alignment check so earlier preparation remains current and exam-focused. For real study planning, the key is to compare the finalized objectives against the course structure, revisit any changed areas, and avoid overstudying draft-only material that no longer appears in the final outline. This update helps students protect their time and keep their preparation aligned with the actual exam blueprint. Produced by BareMetalCyber.com, where you’ll find more cyber audio courses, books, and information to strengthen your educational path. Also, if you want to stay up to date with the latest news, visit DailyCyber.News for a newsletter you can use, and a daily podcast you can commute with. And dont forget Cyberauthor.me for the companion study guide and flash cards!
Full-Course Review: The SY0-801 Memory Map (Review)
Season 2 · Episode 117
Wednesday, July 15, 2026 • Duration 16:42
CURRENT EDITION: Security+. This episode is part of Season 2, the recommended course for the current certification exam.
This episode provides a guided review of the major relationships students should remember across the SY0-801 course. The five-domain structure can be understood as a connected security model: threats and vulnerabilities create risk, risk drives control selection, controls support secure architecture, operations generate evidence, and governance guides repeatable decisions. Students should review core models such as CIA, AAA, defense in depth, Zero Trust, risk treatment, identity lifecycle, incident response, data protection, resilience, and third-party oversight. For the exam, the goal is to see how topics connect rather than treating each objective as a separate vocabulary list. Strong performance comes from recognizing the situation, choosing the right principle, and applying the correct control or process. Produced by BareMetalCyber.com, where you’ll find more cyber audio courses, books, and information to strengthen your educational path. Also, if you want to stay up to date with the latest news, visit DailyCyber.News for a newsletter you can use, and a daily podcast you can commute with. And dont forget Cyberauthor.me for the companion study guide and flash cards!
PBQ Strategy: Turning Objectives into Scenario Decisions (Review)
Season 2 · Episode 116
Wednesday, July 15, 2026 • Duration 15:18
CURRENT EDITION: Security+. This episode is part of Season 2, the recommended course for the current certification exam.
This episode teaches students how to approach performance-based questions by turning exam objectives into practical scenario decisions. A strong PBQ approach starts by identifying the task, the environment, the security goal, and the evidence provided. Students should look for clues such as system type, data sensitivity, user role, log entries, network placement, access requirement, or incident stage before choosing controls or actions. Examples may involve IAM decisions, incident response ordering, firewall rule selection, cloud misconfiguration, log interpretation, data protection, or vulnerability prioritization. For Security+ preparation, the focus is not memorizing isolated facts but applying concepts in context, eliminating unsafe choices, and selecting the most appropriate response for the stated goal. Produced by BareMetalCyber.com, where you’ll find more cyber audio courses, books, and information to strengthen your educational path. Also, if you want to stay up to date with the latest news, visit DailyCyber.News for a newsletter you can use, and a daily podcast you can commute with. And dont forget Cyberauthor.me for the companion study guide and flash cards!
Awareness Delivery and Effectiveness: LMS, Self-Service, Metrics, Behavior Risk Scoring, BEC, BYOD, and Remote Work (5.6)
Season 2 · Episode 115
Wednesday, July 15, 2026 • Duration 14:51
CURRENT EDITION: Security+. This episode is part of Season 2, the recommended course for the current certification exam.
This episode covers how security awareness is delivered, measured, and improved over time. Students should understand learning management systems, self-service training, one-to-one instruction, and one-to-many instruction as different ways to reach users based on scale, role, and need. Effectiveness metrics may include completion rates, phishing simulation results, reporting rates, repeat failures, policy acknowledgements, and behavior risk scoring. Training topics may include social engineering, business email compromise, removable media, bring your own device rules, remote work, and operational security. For Security+ scenarios, the goal is to connect training delivery and measurement to risk reduction, management reporting, and improved user behavior in realistic work environments. Produced by BareMetalCyber.com, where you’ll find more cyber audio courses, books, and information to strengthen your educational path. Also, if you want to stay up to date with the latest news, visit DailyCyber.News for a newsletter you can use, and a daily podcast you can commute with. And dont forget Cyberauthor.me for the companion study guide and flash cards!
Security Awareness Training: Onboarding, Ongoing, Targeted, and Corrective Training (5.6)
Season 2 · Episode 114
Wednesday, July 15, 2026 • Duration 13:12
CURRENT EDITION: Security+. This episode is part of Season 2, the recommended course for the current certification exam.
This episode explains security awareness as an ongoing program rather than a one-time compliance activity. Students should understand onboarding training as the first introduction to organizational expectations, acceptable use, data handling, reporting procedures, and common threats. Ongoing training reinforces important behaviors over time, while targeted training focuses on specific roles, risks, departments, or emerging threats. Corrective training is used when behavior shows a gap, such as repeated phishing failures, improper data handling, unsafe remote work habits, or policy violations. For Security+ scenarios, awareness training should be matched to the risk and audience, with the goal of improving real behavior rather than simply completing a checkbox requirement. Produced by BareMetalCyber.com, where you’ll find more cyber audio courses, books, and information to strengthen your educational path. Also, if you want to stay up to date with the latest news, visit DailyCyber.News for a newsletter you can use, and a daily podcast you can commute with. And dont forget Cyberauthor.me for the companion study guide and flash cards!
Penetration Testing, Reconnaissance, Frameworks, Functional Testing, and Behavioral Testing (5.5)
Season 2 · Episode 113
Wednesday, July 15, 2026 • Duration 14:56
CURRENT EDITION: Security+. This episode is part of Season 2, the recommended course for the current certification exam.
This episode explains penetration testing and related assessment methods at a Security+ level. Students should understand the difference between known, unknown, and partially known environments, where testers may have full information, no internal knowledge, or limited details before testing begins. Reconnaissance may be active, involving direct interaction with targets, or passive, relying on publicly available information and indirect observation. Physical, offensive, defensive, and integrated testing can evaluate different parts of the organization’s security posture. Frameworks and standards help structure testing so results are repeatable and understandable. Functional testing checks whether controls work as designed, while behavioral testing examines how people or systems respond under realistic conditions. Produced by BareMetalCyber.com, where you’ll find more cyber audio courses, books, and information to strengthen your educational path. Also, if you want to stay up to date with the latest news, visit DailyCyber.News for a newsletter you can use, and a daily podcast you can commute with. And dont forget Cyberauthor.me for the companion study guide and flash cards!
Audit Scope and Engagements: Charters, Gap Analysis, Internal Reviews, External Reviews, and Benchmarking (5.5)
Season 2 · Episode 112
Wednesday, July 15, 2026 • Duration 14:41
CURRENT EDITION: Security+. This episode is part of Season 2, the recommended course for the current certification exam.
This episode covers audit scope and engagement planning, including charters, frequency, boundaries, gap analysis, internal reviews, external reviews, regulatory assessments, and benchmarking. Students should understand that an audit charter defines authority, purpose, responsibilities, and scope so the review is properly controlled and understood. Gap analysis compares the current state to a required or desired state, such as a standard, policy, framework, or regulatory expectation. Internal reviews may support self-improvement, while external reviews and regulatory assessments provide independent or required evaluation. Benchmarking compares performance or controls against a known reference. For Security+ scenarios, the key is knowing what is being assessed, why it is being assessed, and what evidence is needed. Produced by BareMetalCyber.com, where you’ll find more cyber audio courses, books, and information to strengthen your educational path. Also, if you want to stay up to date with the latest news, visit DailyCyber.News for a newsletter you can use, and a daily podcast you can commute with. And dont forget Cyberauthor.me for the companion study guide and flash cards!
Audit Data Gathering: Sampling, Questionnaires, Interviews, Assertions, and Reference Sources (5.5)
Season 2 · Episode 111
Wednesday, July 15, 2026 • Duration 13:11
CURRENT EDITION: Security+. This episode is part of Season 2, the recommended course for the current certification exam.
This episode explains how audits and assessments gather evidence to determine whether controls, processes, and security requirements are working as expected. Students should understand sampling as reviewing a representative portion of records or systems rather than every item, while questionnaires and interviews help collect information from control owners, administrators, users, and stakeholders. Assertions are claims about control design, operation, or compliance that must be supported by evidence. Reference sources such as MITRE ATT&CK, the Cyber Kill Chain, and the Diamond Model help organize attacker behavior, incident analysis, and assessment context. For Security+ scenarios, the focus is on gathering reliable evidence, validating claims, and using structured sources to support defensible conclusions. Produced by BareMetalCyber.com, where you’ll find more cyber audio courses, books, and information to strengthen your educational path. Also, if you want to stay up to date with the latest news, visit DailyCyber.News for a newsletter you can use, and a daily podcast you can commute with. And dont forget Cyberauthor.me for the companion study guide and flash cards!
Non-Compliance, Privacy Rights, Legal Holds, Legal Orders, and Retention (5.4)
Season 2 · Episode 110
Wednesday, July 15, 2026 • Duration 15:47
CURRENT EDITION: Security+. This episode is part of Season 2, the recommended course for the current certification exam.
This episode covers the consequences of non-compliance and the legal and privacy concepts that shape data handling decisions. Students should understand that non-compliance can lead to reputational damage, financial penalties, legal action, contract violations, license loss, operational disruption, and loss of customer trust. Privacy rights may include opt-in and opt-out choices, access to personal data, correction of inaccurate data, processing restrictions, and deletion requests where applicable. Controller and processor roles affect who determines the purpose of processing and who acts on instructions. Legal holds preserve relevant information when litigation or investigation is expected, while legal orders may require action or disclosure. For Security+ scenarios, retention requirements must be balanced against disposal, privacy, ownership, and evidence preservation duties. Produced by BareMetalCyber.com, where you’ll find more cyber audio courses, books, and information to strengthen your educational path. Also, if you want to stay up to date with the latest news, visit DailyCyber.News for a newsletter you can use, and a daily podcast you can commute with. And dont forget Cyberauthor.me for the companion study guide and flash cards!
Compliance Training and Monitoring: Data Handling, AML/CTF, Anti-Bribery, and Attestations (5.4)
Season 2 · Episode 109
Wednesday, July 15, 2026 • Duration 14:15
CURRENT EDITION: Security+. This episode is part of Season 2, the recommended course for the current certification exam.
This episode explains compliance as the need to meet laws, regulations, contracts, internal policies, and industry standards. Students should understand that compliance training helps employees know what is required for data handling, privacy, reporting, acceptable behavior, and regulated business activity. Anti-money laundering and counter-terrorist financing controls focus on detecting and preventing misuse of financial systems, while anti-bribery requirements address improper payments, gifts, influence, and conflicts. Monitoring helps verify that required controls are followed, and attestations or acknowledgements create evidence that users, vendors, or employees have received, understood, or accepted obligations. For Security+ scenarios, compliance is not just paperwork; it is a control system that supports accountability and reduces legal, financial, and reputational risk. Produced by BareMetalCyber.com, where you’ll find more cyber audio courses, books, and information to strengthen your educational path. Also, if you want to stay up to date with the latest news, visit DailyCyber.News for a newsletter you can use, and a daily podcast you can commute with. And dont forget Cyberauthor.me for the companion study guide and flash cards!